 Featured
TP-Link Deco BE11000 Vulnerability: Update Your Firmware Now
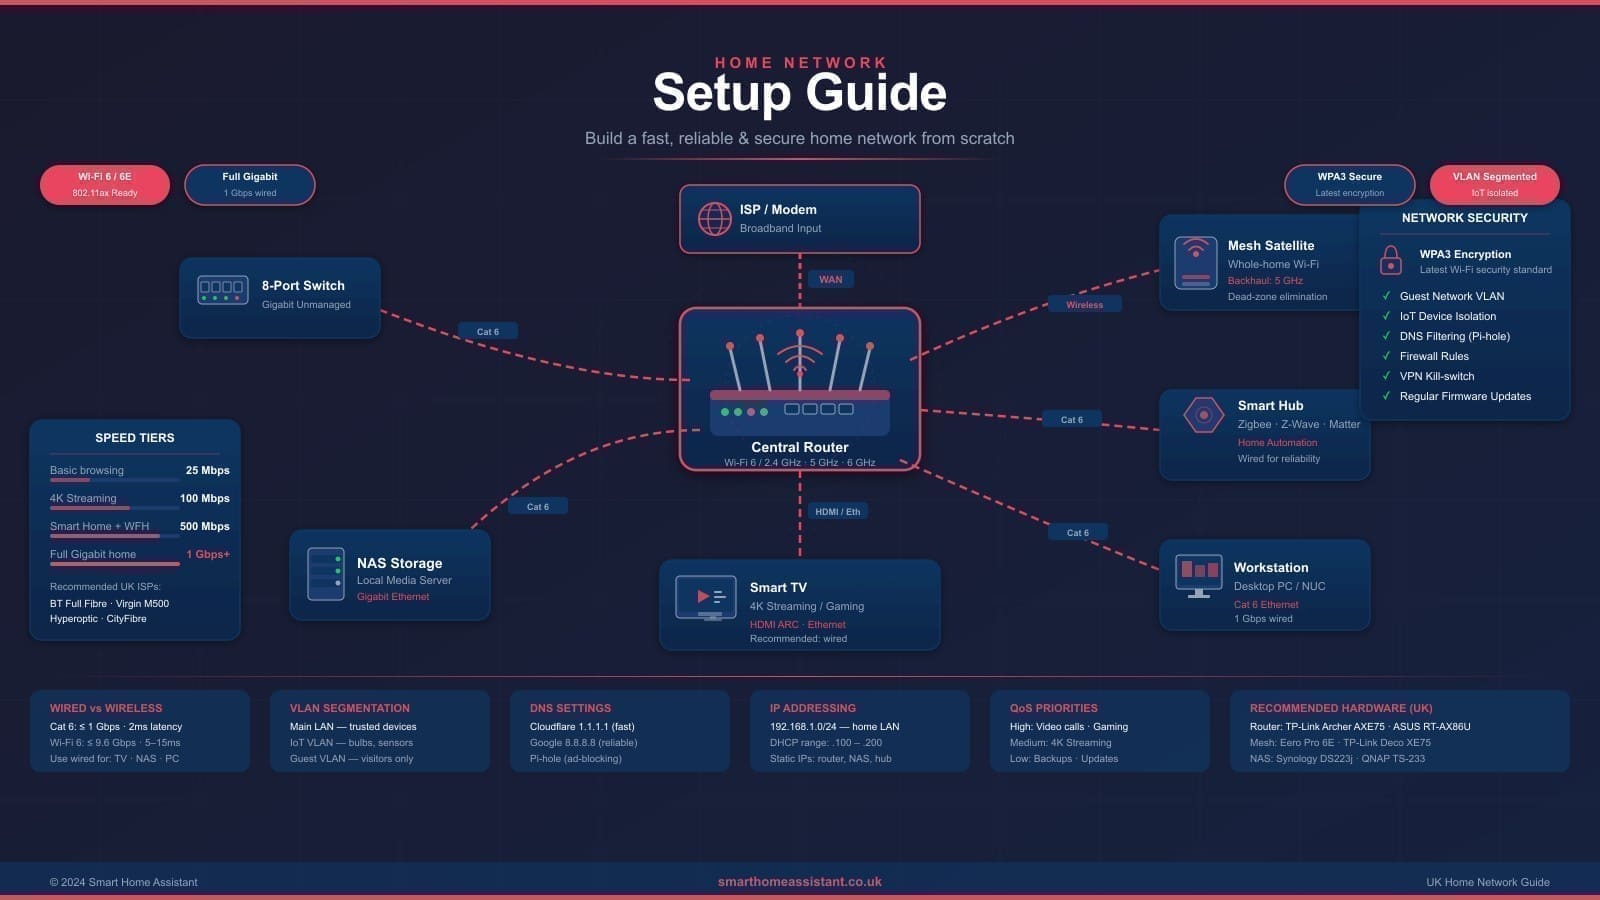
TP-Link has disclosed a high-severity OS command injection flaw in the Deco BE11000 mesh Wi-Fi 7 system, tracked as CVE-2026-17176. A crafted UDP packet sent from another device on the same network can give an attacker root-level control of the router. A fixed firmware build is already available. Here's what happened, why it matters if your Deco sits at the centre of a Home Assistant or other smart home network, and exactly how to update.
By Sepehr